Proof Over Promises
for AI Agents That Touch Production.
The Cryptographic Proof & Execution Gate for AI Agents. Your AI agents write production code, run shell commands, query live databases, and invoke remote MCP tools while your teams trust their output.
KTOS provides an uncompromising execution membrane: zero-trust agent passports, runtime MCP mediation, host-level PTY enclaves, and cryptographic evidence objects (AEOs) your auditors and regulators can verify independently—without trusting our servers.
Built for Any Model, Agent Runtime & Cloud Enclave
KTOS brokers execution across your AI agent fleets without vendor lock-in. Encapsulates tool calls, prompts, and shell executions into FIPS 204 ML-DSA-65 signed Agent Evidence Objects.
* Logos are trademarks of their respective owners. Listing here reflects integration compatibility and runtime mediation, and does not imply endorsement, sponsorship, or certification by any company shown.
Five Steps to Provable Trust
KTOS is the first platform to close the full loop: intercept → guard → scan → remediate → attest. Every action signed. Every state change proven.
Intercept
KTOS Enclave & Profile
Captures AI agent intent and MCP JSON-RPC calls before execution. Canonical PTY supervisor with keystroke attestation.
Guard
KTOS Guard & SEKHEM
Post-quantum L7 WAF. Rotating Kyber-1024 vaults. Dihedral D₈ polymorphic argument scrubbing. Zero-day prompt injection blocked.
Scan
KTOS Scan & OmniScan
OmniScan 8-lane sweep: Shadow AI discovery, Plugin4Shell audit, STIG CAT I/II, SBOM/KEV correlation, and secret scanning across the full asset boundary.
Remediate
KTOS Heal & Comply
Closed-loop ASAF engine applying host remediations under a human gate. APDL declarations compile to Ansible. FIPS kernel enforced.
Attest
KTOS Attest & Stream
Every state change anchored in ML-DSA-65 signed DAG ledger. Streaming OCSF findings to Splunk and Axonius. Assessment-ready evidence (self-assessment or C3PAO).
Architectural Control Plane: Central Governance, Bare-Metal Proof
Decide in one place, verify mathematically everywhere else. KTOS enforces strict execution boundaries where autonomous AI agents touch production.
Layer 4 · KTOS-MCP Master-Kernel
Intercepts JSON-RPC stdio and mTLS SSE sessions from Claude Code, Cursor, and Antigravity IDE before execution.
100.00% Neutralization Across All Three Autonomous Pentest Engines
Internal adversarial testing by the NouchiX team using CyberStryke, AgentHound, and HexStrike AI. Not a third-party audit.
Rigorous adversarial verification executing 92 targeted attack patterns across three independent security engines: CyberStryke Automated Assault (30/30 OWASP API & LLM vectors), AgentHound Offensive Security Framework (28/28 agentic attack paths across MCP, A2A, model gateways, vector DBs, and execution sandboxes), and HexStrike AI Autonomous Red Team Battery (34/34 FastMCP fuzzing, Nuclei SSTI, Metasploit stagers, Sqlmap stacked/OOB injections, SUID escapes, and covert C2 tunnels). All 92 vectors intercepted, scrubbed, or quarantined in real-time with zero false passes.
OWASP API Top 10 & OWASP LLM Top 10 Neutralization
Validates edge resilience against classic web API threats and LLM prompt compromise. Neutralizes SQL Injection, Cross-Site Scripting (XSS), Directory Traversal, Null Byte Escapes, System Prompt Leaks, and Egress Token Disclosure via SEKHEM L7 WAF.
BloodHound for the Agentic Stack (MCP, A2A & Inference Mesh)
Adversarial framework targeting agentic attack graphs across MCP servers, A2A protocols, model gateways (LiteLLM), inference backends (Ollama/vLLM), and vector DBs (Qdrant). Neutralizes Tool Shadowing, Description Poisoning, Identity Forgery, and IFC Taints.
Automated Multi-Agent Red Team & Exploit Synthesis
Executes high-density adversarial exploit chains against FastMCP interfaces, testing for schema fuzzing, Metasploit payload delivery, SQLMap stacked/OOB channels, Nuclei template injections, SUID privilege escalations, and stealth C2 beacons.
SQL Injection & Parameter Tampering
Union-based extractions, blind boolean injections, and out-of-band SQLi payloads completely scrubbed and blocked.
Cross-Site Scripting (XSS & Polyglots)
Reflected DOM injections, mutated SVG vectors, and script tag payloads neutralized prior to execution.
Path Traversal & Null Byte Escapes
Dot-dot-slash directory traversal (/../etc/shadow) and %00 null byte bypasses intercepted and contained in sandbox.
MCP Tool Description Poisoning & Shadowing
Adversarial instruction injection hidden in tool parameter docstrings and tool shadowing collisions neutralized by AST schema lockdown.
A2A Impersonation & Identity Spoofing
Subagent forgery and caller spoofing attempts blocked via Nkyinkyim-bound ML-DSA-65 Agent Passports and cryptographic nonces.
IFC Violation, Taints & Secret Exfiltration
Context window taint propagation, vector DB token leakage, and side-channel exfiltration severed by Zero-Egress Blackhole.
FastMCP Schema Fuzzing & Malformed Frames
Malformed JSON-RPC frames, parameter type confusion, and unicode payload smuggling intercepted by AST validation and schema lock.
Nuclei SSTI & Metasploit Stager Payloads
Server-side template injections, reverse TCP stager shellcode, and memory injection sequences caught by SEKHEM Gateway and PTY enclave.
SUID Privilege Escalation & Covert C2 Egress
SUID/Sudo process escapes, GTFOBins exploitation, DNS/SMB tunneling, and covert beaconing severed by Layer 1 Giza Firewall.
Lineage You Can Prove. Step by Step.
Standard logs tell you an action occurred. Lineation tells you why in their cloud database. KTOS gives you mathematical non-repudiation on your own bare-metal host.
Staging Mirror & Human Gate
Pre-flight dry-run executes in an isolated mirror staging environment. Config diff generated; CISO human gate approves execution.
{
  "diff": "- crypto.fips_enabled = 0\n+ crypto.fips_enabled = 1",
  "gate": "HUMAN_APPROVAL_REQUIRED",
  "approver": "CISO / Security Lead",
  "staging_status": "PASS_NO_REGRESSION"
}One Platform. Complete Trust.
Every module is post-quantum signed, DAG-attested, and sovereignty-auditable. Mix and match by deployment tier.
Every AI agent action signed with ML-DSA-65 and anchored in an immutable DAG ledger. Cryptographically impossible to backdate.
Portable ML-DSA-65 identity credential for AI agents. Binds intent + action + outcome in a verifiable Agent Evidence Object (AEO).
Full deterministic replay of any AI agent session. Reproduce exact tool calls, arguments, and outputs for incident investigation.
Continuous behavioral trust scoring across agent fleets. Anomaly detection powered by KASA evolutionary algorithm.
8 scanning lanes: Shadow AI discovery (Ollama/vLLM), Plugin4Shell audit, STIG CAT I/II checks, SBOM/KEV correlation, secret scanning.
Post-quantum L7 WAF with rotating CRYSTALS-Kyber-1024 vaults (pre-standard; FIPS 203 ML-KEM-1024 migration in progress) and polymorphic argument scrubbing.
Deep packet inspection of MCP JSON-RPC sessions. Flags prompt injections, indirect tool abuse, and cross-agent privilege escalation.
Canonical PTY supervisor wrapping every AI agent shell session. Keystroke attestation + isolation boundary enforcement.
110 CMMC L2 practices + 36,195 cross-framework mappings. APDL policy declarations compile to Ansible. Assessment-ready evidence (self-assessment or C3PAO).
ML-DSA-65 authorized kernel-level remediation: sysctl, PAM, SELinux, GRUB FIPS. Human gate required. DAG-attested on execution.
Formal mathematical verification of compliance policies using Z3 SMT solver. Proves policy satisfiability before deployment.
Real-time OCSF 1.0 event stream to Splunk HEC, Elastic/Filebeat, and Axonius DSPM. Every DAG event surfaces in your SOC.
The Only Platform That Closes the Loop
SaaS proxies trap logs in vendor clouds. Cloud scanners ignore agent keystrokes. GRC checklists verify paperwork. KTOS is the only platform providing host execution gating and vendor-independent post-quantum proof.
| Capability ↓ / Vendor → | KTOS NouchiX | Lineation Agent Gateway | Palo Alto Protect AI | SentinelOne Prompt Sec | Snyk Invariant | Wiz Cloud CSPM | SteelCloud ConfigOS | Vanta / Drata GRC Checklists | Patero Packet Encrypt | NVIDIA OpenShell |
|---|---|---|---|---|---|---|---|---|---|---|
Primary Focus autonomous agent execution vs legacy tooling | ◑ | — | — | — | — | — | — | — | ◑ | |
MCP Protocol Mediation deep JSON-RPC + PTY inspection | ◑ | — | ◑ | — | — | — | — | — | ||
Host / Terminal Enclave PTY enclave, subprocess, PAM/sysctl | — | — | — | — | — | — | — | |||
Human-in-the-Loop Gating isolated staging mirror → signed apply | ◑ | — | ◑ | — | — | — | — | — | ◑ | |
Audit Trail Architecture immutable content-addressed DAG | ◑ | — | — | — | — | ◑ | — | — | ◑ | |
Cryptographic Verifiability FIPS 204 ML-DSA-65 (vendor-independent) | — | — | — | — | — | — | — | — | ◑ | |
Air-Gap / Zero-Egress native sovereign bare-metal (zero external APIs) | ◑ | — | — | — | — | ◑ | — | ◑ | ||
DoD / CMMC / FCA Defense 36,195 STIG/CMMC mappings + signed AEO | — | — | — | — | — | — | — | — | ||
Offline Verifier available to design partners | — | — | — | — | — | — | — | — | ◑ | |
Shadow AI Discovery Ollama, vLLM, rogue LLM endpoints | ◑ | ◑ | — | — | — | — | — | — | ◑ | |
SIEM / OCSF Stream Splunk HEC, Elastic, Axonius DSPM | ◑ | — | — | — | — | — |
“78% of organizations have already had an AI security incident[1], and nearly half can't trace what their AI did[2]. When an AI agent changes production, 'trust our logs' isn't an answer. Proof is. KTOS signs every agent action at the moment it happens, so anyone can verify what happened — without trusting us.”
Built for the Hardest Problems
Defensible Self-Attestation
Every SPRS score and self-assessment backed by signed, independently verifiable evidence: OSCAL-formatted SSP, POA&M analysis, traceability matrix, and a signed manifest. Ready for a C3PAO the day your prime or contract requires one.
Autonomous Agentic SOC
Enterprise security teams wrap their Claude, Cursor, and Antigravity agent fleets with KTOS. Every tool call attested. Anomaly scores computed. Incidents replayed forensically. SOAR playbooks staged for human approval.
Stargate CMMC Autopilot
Sovereign air-gapped compliance autopilot. APDL declarations compile to Ansible. PAM, SELinux, kernel FIPS enforced autonomously under a human approval gate. DAG-attested on every execution. Zero telemetry. Bare-metal.
KHEPRA Trust OS (KTOS) Pricing
Every KTOS product runs on the same patent-pending KHEPRA Protocol. Pick the product that answers your question. Platform tiers activate instantly through Stripe. Enterprise and Sovereign deployments run air-gapped on your own bare metal.
KTOS CMMC Hub & Fleet Engine
“Can I prove what I attested?”
For: CISO · Compliance Lead · Contracts Officer (DIB)
- Desktop App, Fleet Hub & osquery Fleet Remote Engine
- Sovereign bare-metal scans (zero egress)
- APDL staging & human-gated remediation
- Assessment-ready OSCAL / SSP / POA&M evidence packages
Fleet Hub + ASAF Remediation Daemon + assessment export
Air-gapped, FIPS 140-3 inheritance in progress, SDVOSB-eligible sole-source
KTOS Agentic SOC
“What did my AI agents do, and can I prove it?”
For: Security Engineer · Platform Lead · Startup CTO
- Agentic SOC SaaS platform
- Continuous Flight Recorder SDK
- KASA behavioral anomaly detector
- ML-DSA-65 signed SOAR playbooks · multi-agent orchestration
Self-serve via Stripe · OmniScan + Flight Recorder
Full SOAR engine, team seats + RBAC
KTOS-MCP Master-Kernel
100 native tools, ML-DSA-65 post-quantum signing, SEKHEM L7 WAF prompt defense, and Windows Event Viewer logging. One license key unlocks the kernel from Community to Sovereign.
Community
The sovereign trust kernel. 4 Core Trust Modules. Local SQLite Ledger.
- 500 Tokenomics credits
- 4 core trust modules
- 9 base MCP tools
- Local SQLite ledger
- ML-DSA-65 signing
- PQC key generation
- Flight recorder (7-day)
- GHCR container image
Platform
Self-serve KTOS — Full OmniScan (50+ Detectors) + threat detection.
- 3,000 Tokenomics credits
- Everything in Community
- OmniScan (50+ Detectors across 8 lanes)
- Shadow AI discovery
- Plugin4Shell audit
- STIGViewer API integration
- OCSF SIEM telemetry stream
- Agent anomaly alerts (Slack/PD)
- Unlimited DAG history
Enterprise
Full Agentic SOC with remediation daemon & SEKHEM L7 PQC-WAF.
- 15,000 Tokenomics credits
- Everything in Platform
- Full Agentic SOC
- SEKHEM L7 PQC-WAF
- PTY Enclave supervisor
- ASAF Remediation Daemon
- Z3 SMT formal proof
- DataLoop self-healing
- Team seats + RBAC
- SOC 2 / EU AI Act evidence
Sovereign
Air-gapped. Bare-metal. SDVOSB-eligible. Zero egress.
- 100,000+ Tokenomics credits
- Everything in Enterprise
- Air-gapped static binaries
- FIPS 140-3 module inheritance (in progress)
- Zero-egress enforcement
- APDL compiler + policy editor
- Dedicated assessment evidence engineering
- SDVOSB-eligible sole-source package
- Iron Bank / k8s deployment
Built by a Veteran.
Engineered for Proof.
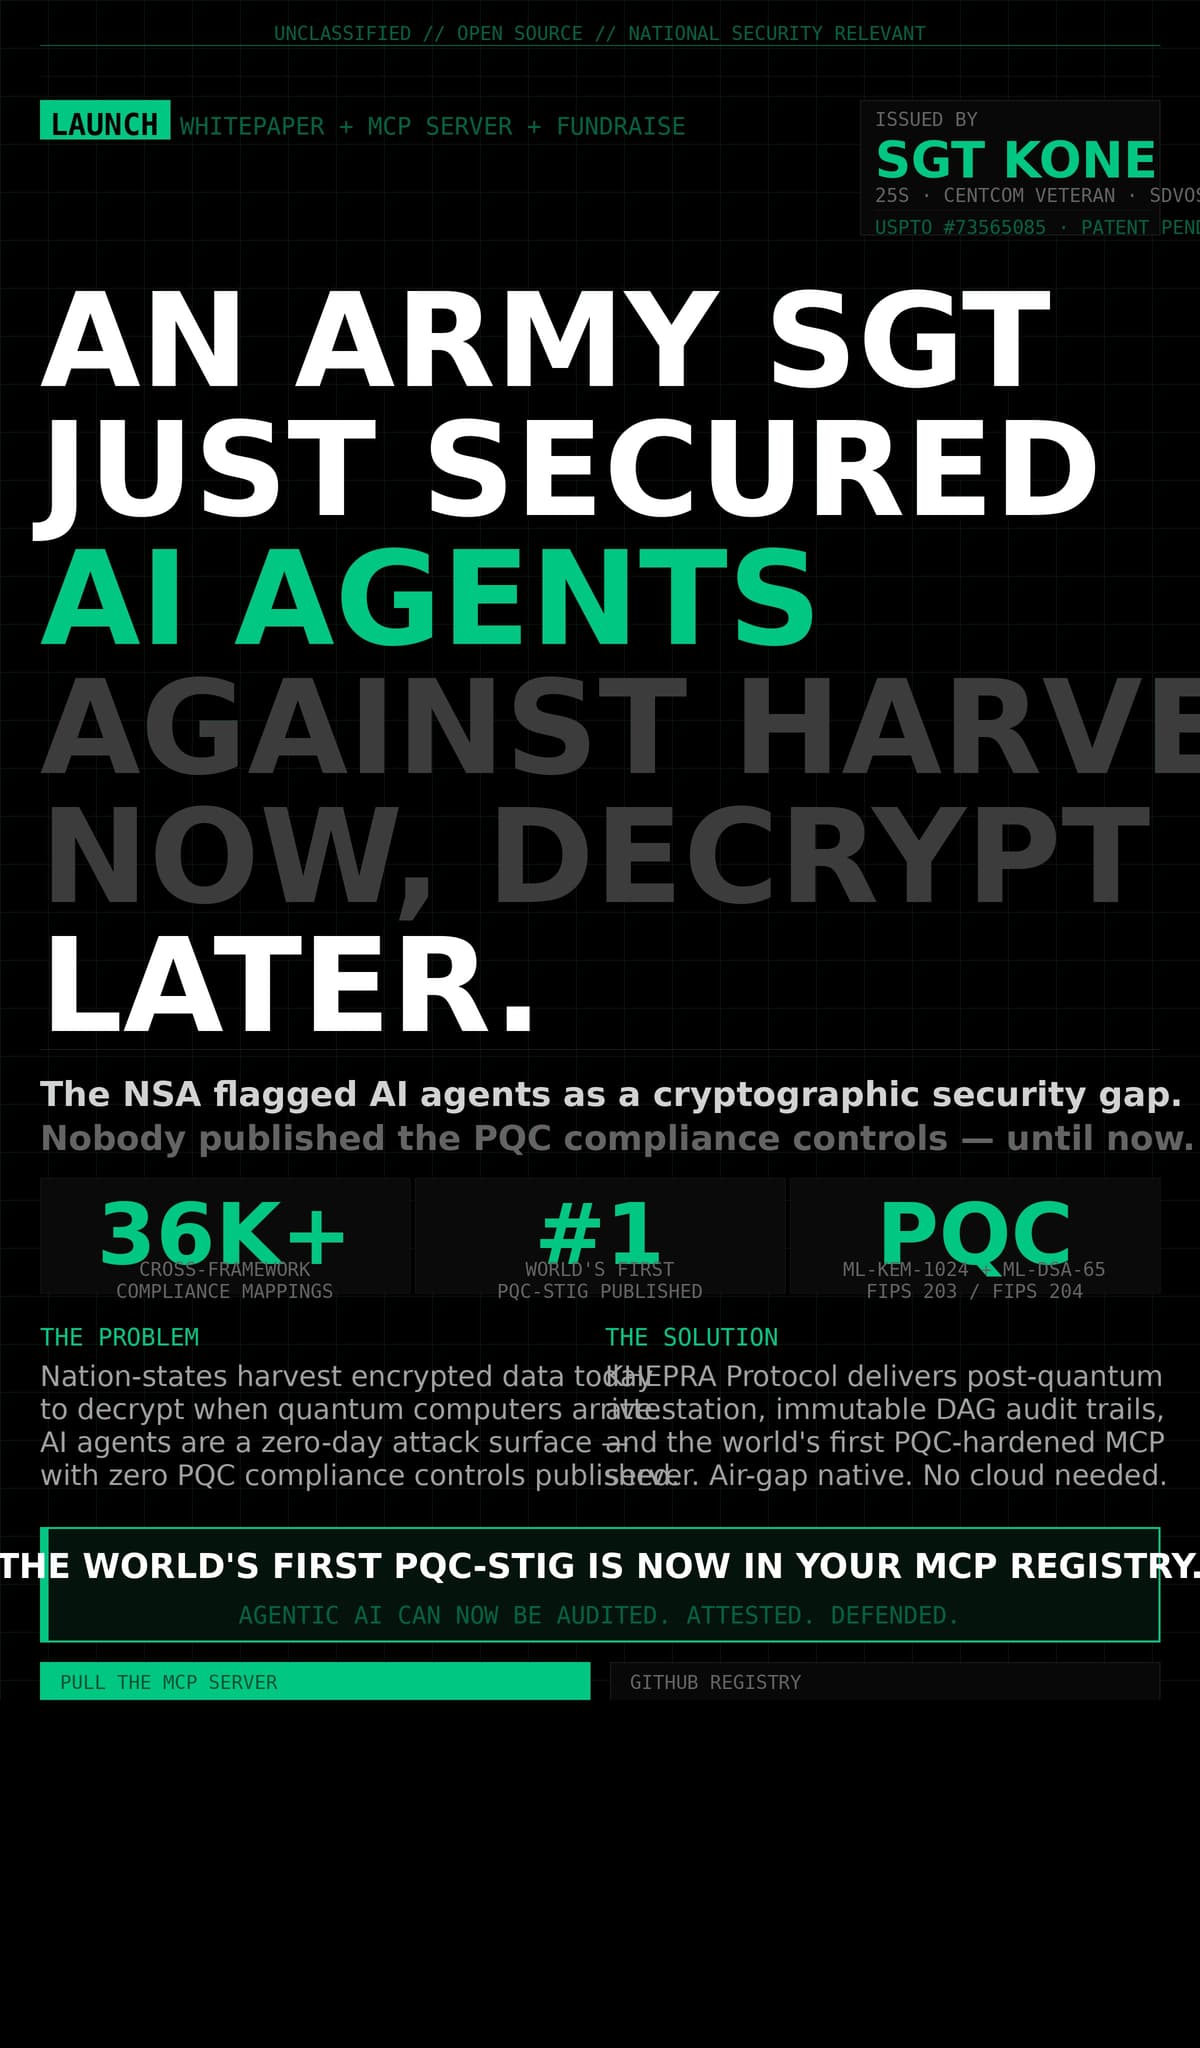
SecRed Knowledge Inc. d/b/a NouchiX is a Service-Disabled Veteran-Owned Small Business (SDVOSB-eligible) founded by Army Signal Corps Sergeant Souhimbou “Cyber” Doh Kone — 25S SATCOM, active Secret clearance, M.S. Digital Forensics & Cybersecurity (NSA CAE-CDE).
The KHEPRA Protocol (USPTO #73565085) is the sovereign trust kernel under every NouchiX product. It is never sold directly — it is the moat.
I AM SOUHIMBOU
The AI Security Architect For Your Agentic SOC · KTOS Agentic SOC
Ready to Prove It?
Schedule a sovereign demo. See your AI agent activity attested in real time. Get your SPRS score projection. Walk away with an assessment-ready evidence package.